
Learn Ethical Hacking
Learn Ethical Hacking — A penetration testing hacking course with hands-on labs
Learn Ethical Hacking is a free-to-start hacking course for iPhone and Android that follows the order of a real penetration test: recon, scanning, exploitation, privilege escalation and reporting. Short lessons teach the method, pentest labs on simulated targets make you use it, and a graded exam ends in a certificate of completion.
- Price
- Free, Pro upgrade
- Platforms
- iOS and Android
- Languages
- 22
- Age rating
- 4+
- Version
- 81.3.0
- Requires
- iOS 15.1 or later
- App Store
- 5.0 ★ (5)
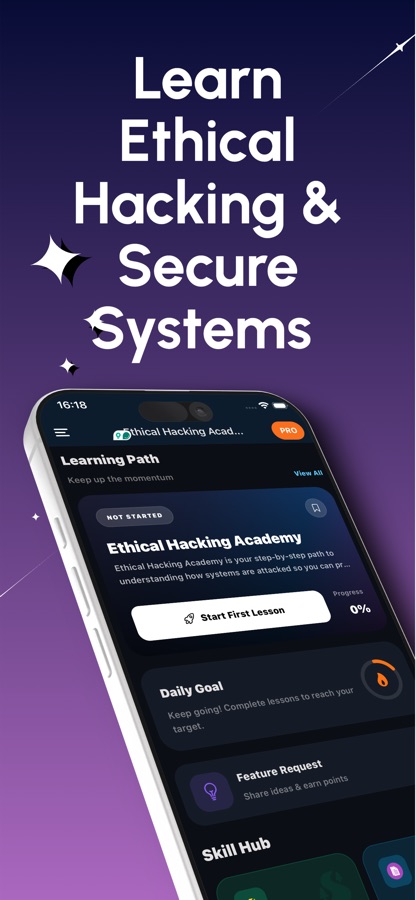
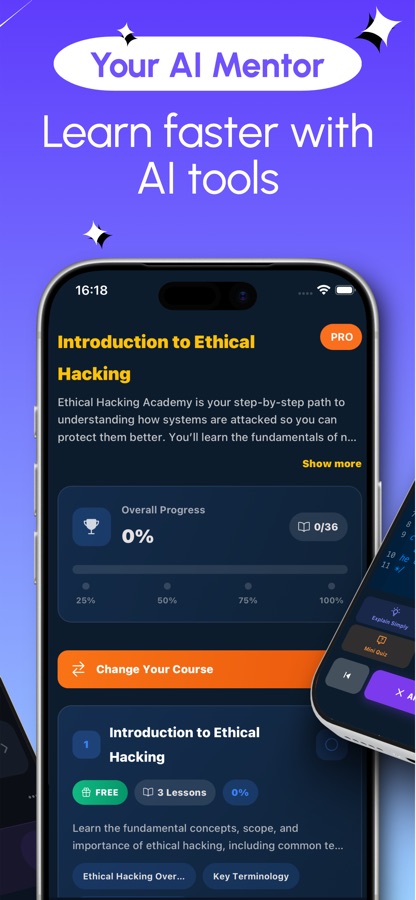
Learn the attack so you can write the defence.
Every lab runs against a simulated, sandboxed target, so you can type the commands, read the output and make mistakes with nothing real at stake. The skills are offensive, the purpose is to defend, audit and report, and you only ever test systems you own or have written permission to test.
What it is
Learn Ethical Hacking is a mobile penetration testing course for iOS and Android with 30+ courses and 110+ lessons that follow the phases of a real security assessment. It covers Kali Linux, Nmap, Metasploit, Burp Suite, password cracking, web application attacks, privilege escalation, Active Directory, wireless and cloud pentesting, bug bounty hunting and report writing, and each topic is paired with practice on simulated targets. No prior hacking experience is needed.
Kali Linux, Metasploit, Burp Suite and the other tool names mentioned belong to their owners. This app is not affiliated with or endorsed by them..
Inside the app
What it looks like
The course
What the ethical hacking course covers
The site's Learn Ethical Hacking course has 31 courses; these are the ones that make up the spine of a first pass.
Setting Up a Hacking Lab and Linux for Hackers
Virtualization basics, installing Kali Linux, the Linux file system and the essential commands you will use in every later course.
Networking Fundamentals, Cryptography and Windows Internals
How data travels and which protocols matter, the difference between encoding and encryption, hashing, and the architecture and registry of Windows.
Footprinting, Scanning and Nmap Deep Dive
Gathering intelligence on a target, then host discovery, port scanning techniques and enumeration of the services you find.
Metasploit, Burp Suite and Password Cracking
The Metasploit framework's architecture and exploit workflow, proxying and replaying web requests in Burp Suite, and wordlists, rules and Hashcat.
Privilege Escalation and Active Directory Attacks
Enumeration, SUID and sudo abuse on Linux, service misconfigurations on Windows, and Active Directory fundamentals through Kerberoasting.
Web, Wireless, Mobile and Cloud Pentesting
Web application hacking, wireless network testing, Android app analysis and the cloud attack surface including IAM misconfigurations.
Bug Bounty Hunting and Penetration Testing & Reporting
Choosing targets and running recon at scale, then bringing the skills together in a structured test and a report a client can act on.
How it works
How a study session works
The app splits learning from doing, so each topic is a short lesson followed straight away by something to run, predict or fix.
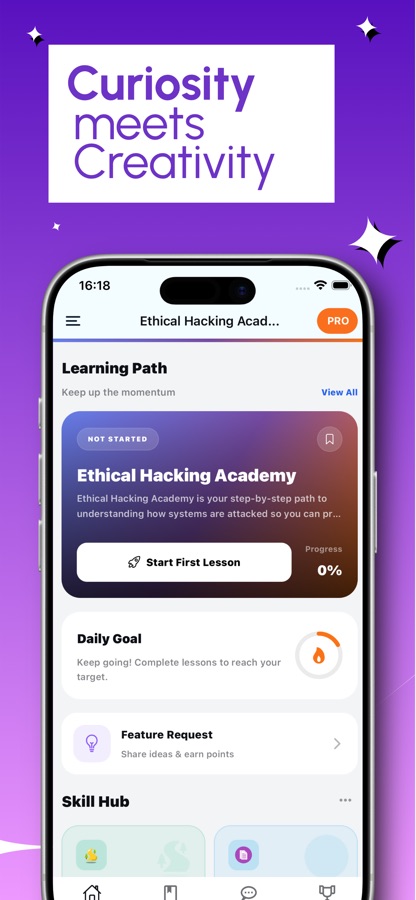
Learn the method in a short lesson
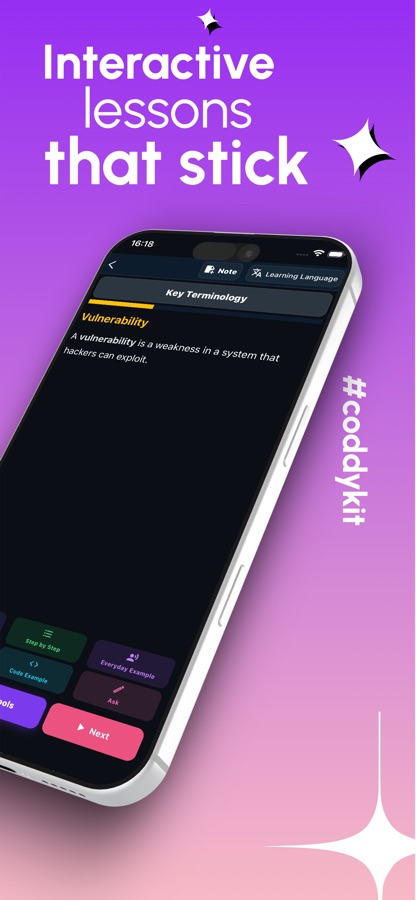
Pick a course from the learning path and read a lesson written in plain language, with an AI mentor ready to explain any tool, technique or error message you do not follow.
Practise on a simulated target
In a pentest lab you work a guided mission step by step: type the commands, read the output and work towards the objective, with hints when you stall. Command drills check whether your flags would actually work.
Review, compete and certify
Quizzes, review cards, cheat sheets and a command book keep earlier material fresh. The live arena and head-to-head matches add competition, and the graded exam issues a certificate with a verification code.
What's inside
What comes with the app
30+
Courses, 110+ lessons
From setting up a safe lab with Kali Linux and Linux for hackers through networking, cryptography and Windows internals to Active Directory attacks, mobile and cloud pentesting and buffer overflow basics.
Labs
Pentest labs on simulated targets
Guided missions where you type the commands and read the output yourself, plus command drills for nmap, gobuster, sqlmap, hydra and john that test whether your flags hold up.
AI
AI mentor
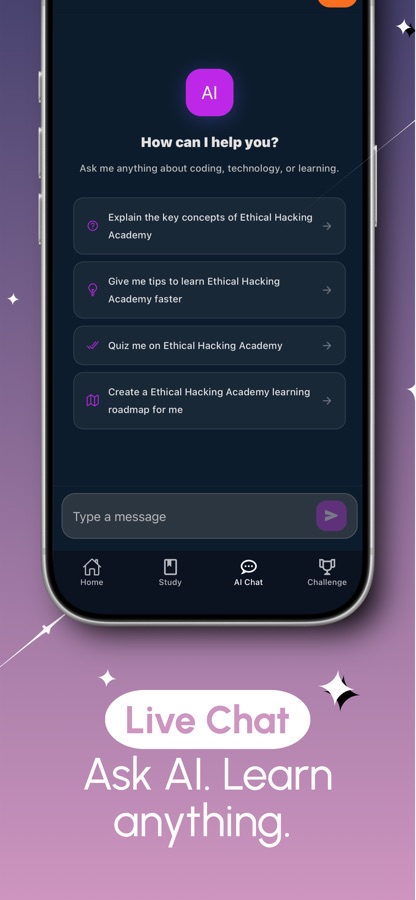
Ask about any tool, technique or error and get a clear explanation. The mentor is part of Pro.
Toolbox
Flag Lab and Hash & Encoding Lab
Switch a tool's flags on and off to see what each does, and identify a hash, peel back encoding layers and choose a wordlist strategy.
Arena
Live arena and head-to-head
A worldwide round runs three times a day, and you can face another learner in a head-to-head match.
Exam
Graded exam and certificate
The final exam issues a certificate of completion with a verification code anyone can check. It is a certificate from this app, not a third-party certification.
Background
What is a penetration test, and what happens in each phase?
A penetration test is an authorised, scoped attempt to break into a system so its owner can fix the weaknesses before a real attacker finds them. It is run in a fixed order so that the result is a report someone can act on rather than a pile of tricks. Learning that order first is what separates a security practitioner from someone who has only collected tools.
Reconnaissancelearn the target first
The tester gathers what is publicly known about the target: domains, staff, technologies and exposed services. Open-source intelligence (OSINT) and footprinting happen here, before any packet is sent that could raise an alarm.
Scanning and enumerationfind the open doors
Tools such as Nmap map which hosts are alive, which ports answer and which service versions are running. Enumeration then asks each service for more detail, because an old version banner is often the first real lead.
Exploitation and privilege escalationprove the weakness is real
A confirmed vulnerability is used to gain a foothold, usually as a low-privileged user. Escalation then looks for misconfigurations, such as weak sudo rules or unquoted service paths, that turn that foothold into administrator access.
Reportingthe part clients pay for
Each finding is written up with evidence, a severity rating and a concrete fix. A technically brilliant test with a vague report changes nothing, which is why reporting is taught as a skill in its own right.
Fit
Who it's for — and who it isn't
A good fit if you
- Are a beginner drawn to cyber security who does not know where to start
- Work in IT or networking and want pentesting skills for your resume
- Are preparing for CTFs, bug bounty programmes or entry-level security exams
- Are a developer who wants to see how attackers break the code you write
- Learn best by typing commands into a safe lab rather than watching videos
Not the right tool if you
- Want to attack systems you do not own, since the course teaches authorised testing only
- Expect a third-party certification, because the certificate is a completion certificate from the app
- Want everything free, as the first course and the first labs are free and Pro unlocks the rest
- Need a full desktop lab with real virtual machines, which still means a laptop
Questions
Frequently asked questions
What is the best app for a hacking course on a phone?
Look for one that follows a real penetration test from recon to reporting and makes you practise, not just read. Learn Ethical Hacking has 30+ courses and 110+ lessons that follow that order, plus pentest labs on simulated targets, command drills and a graded exam. It is free to start on iOS and Android.
Is it legal to learn ethical hacking?
Learning the techniques is legal. Using them on systems you do not own, or without written permission, is not. Learn Ethical Hacking runs every lab against a simulated, sandboxed target and states clearly that you should only test systems you own or are authorised to test.
Do I need to know Linux or networking before I start?
No prior hacking experience is needed. Learn Ethical Hacking begins with what ethical hacking is, the legal ground rules and setting up a safe lab with Kali Linux, then teaches Linux for hackers and networking fundamentals before scanning and exploitation.
What tools does the course teach?
Learn Ethical Hacking covers Kali Linux, Nmap, Metasploit, Burp Suite, Hashcat and John the Ripper, with command drills for nmap, gobuster, sqlmap, hydra and john. The point is knowing which tool answers which question at each stage of a test.
How do the pentest labs work on a phone?
Each pentest lab is a guided mission against a simulated target. You type the commands, read the output and work through the objective step by step, with hints when you stall. A Findings feature then turns what you found into a finding card, the way a pentest report does.
Does Learn Ethical Hacking prepare me for bug bounty hunting?
It gives you the groundwork. A dedicated Bug Bounty Hunting course covers choosing targets, recon at scale and finding common bugs, and the web courses cover SQL injection and XSS. Real programmes have their own rules and scopes, so you read those before testing anything.
Is Learn Ethical Hacking free?
It is free to download. The first course is free in full and the first labs of the catalogue are open. Pro unlocks every course and lab, the AI mentor, the certification exam and removes banner ads.
Is the certificate a recognised security certification?
No. Passing the graded exam earns a certificate of completion from the app, with a verification code anyone can check. It is evidence of the work you did and useful alongside projects, but it is not a third-party certification.
Can I practise against other learners?
Yes. The live arena runs a worldwide round three times a day, and head-to-head matches pit you against another learner. Quizzes, review cards, interview questions, cheat sheets and a glossary are there for solo revision.
Which languages and platforms does it support?
Learn Ethical Hacking runs on iOS and Android and is available in 22 languages. It is rated 4+ on the App Store and needs iOS 15.1 or later on iPhone.
Get started
Run your first lab today
Free to start on iOS and Android, in 22 languages.
More from CoddyKit
Available on iOS and Android.