
एथिकल हैकिंग सीखें
एथिकल हैकिंग सीखें — हैंड्स-ऑन लैब्स वाला penetration testing hacking course
एथिकल हैकिंग सीखें iPhone और Android के लिए एक फ्री-टू-स्टार्ट hacking course है, जो असली penetration test के क्रम का पालन करता है: recon, scanning, exploitation, privilege escalation और reporting। छोटे lessons तरीका सिखाते हैं, simulated targets पर pentest labs आपको उसका इस्तेमाल करने का अभ्यास कराती हैं, और graded exam certificate of completion के साथ समाप्त होता है।
- कीमत
- मुफ्त, Pro upgrade
- प्लेटफ़ॉर्म
- iOS और Android
- भाषाएँ
- 22
- आयु रेटिंग
- 4+
- वर्ज़न
- 81.3.0
- आवश्यकताएँ
- iOS 15.1 या बाद का
- App Store
- 5.0 ★ (5)
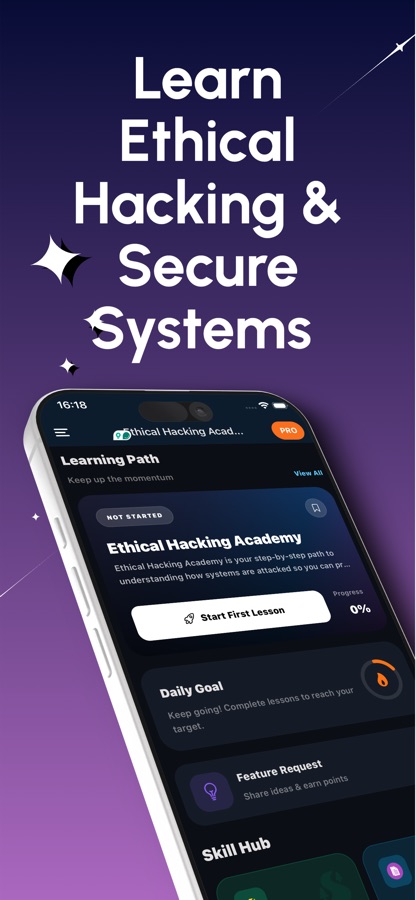
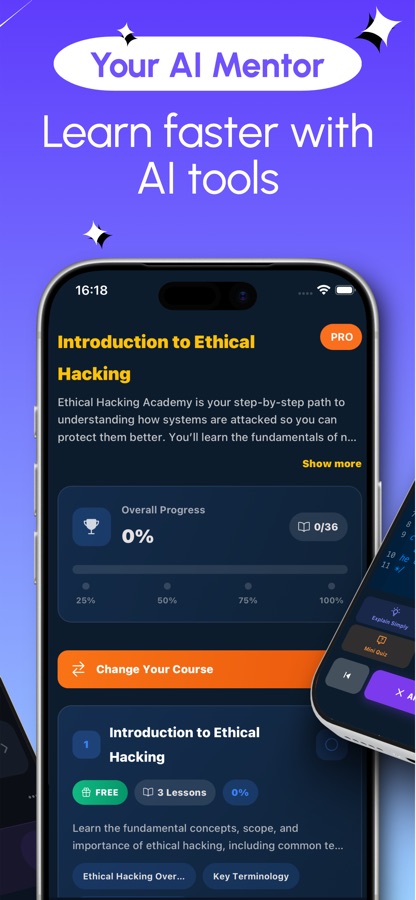
हमले का तरीका सीखें, ताकि आप बचाव लिख सकें।
हर lab simulated, sandboxed target पर चलती है, इसलिए आप commands टाइप कर सकते हैं, output पढ़ सकते हैं और ऐसी गलतियाँ कर सकते हैं जिनसे वास्तविक दुनिया में कुछ भी जोखिम में नहीं पड़ता। कौशल offensive हैं, उद्देश्य defend, audit और report करना है, और आप केवल उन्हीं systems का test करते हैं जिनके आप मालिक हैं या जिनका test करने की लिखित अनुमति आपके पास है।
यह क्या है
एथिकल हैकिंग सीखें, iOS और Android के लिए mobile penetration testing course है, जिसमें 30+ courses और 110+ lessons हैं, जो असली security assessment के phases का पालन करते हैं। इसमें Kali Linux, Nmap, Metasploit, Burp Suite, password cracking, web application attacks, privilege escalation, Active Directory, wireless और cloud pentesting, bug bounty hunting और report writing शामिल हैं, और हर topic को simulated targets पर practice के साथ जोड़ा गया है। hacking का कोई पिछला अनुभव आवश्यक नहीं है।
Kali Linux, Metasploit, Burp Suite और यहाँ बताए गए अन्य tool names उनके owners के हैं। यह app उनसे affiliated नहीं है और न ही उनका endorsement प्राप्त है।.
ऐप के अंदर
यह कैसा दिखता है
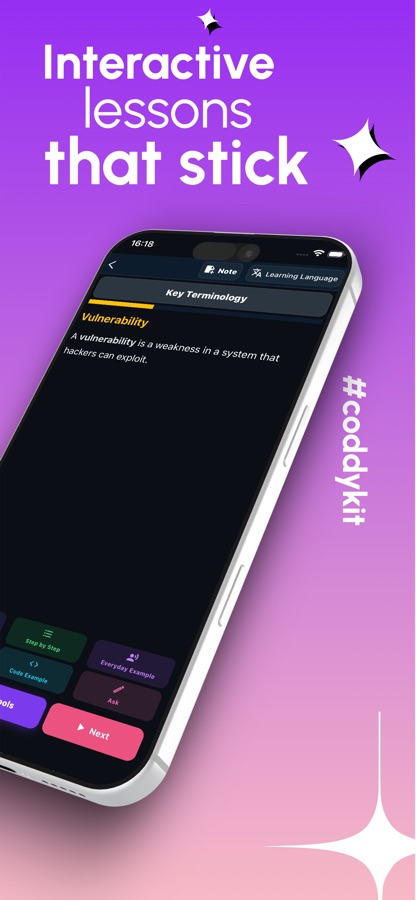
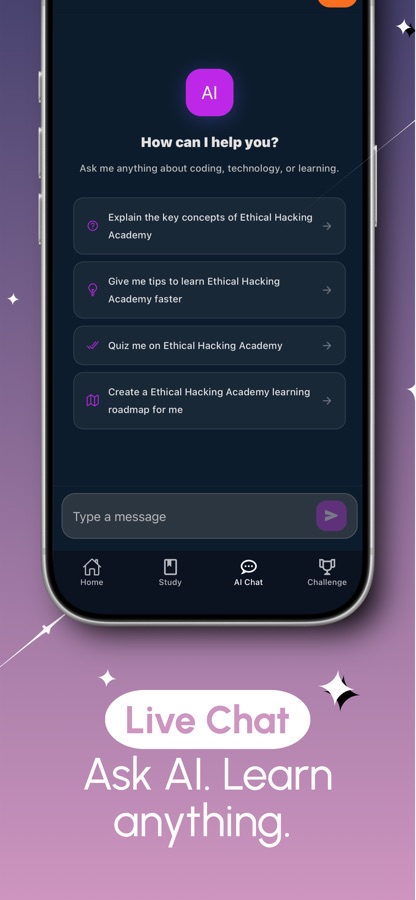
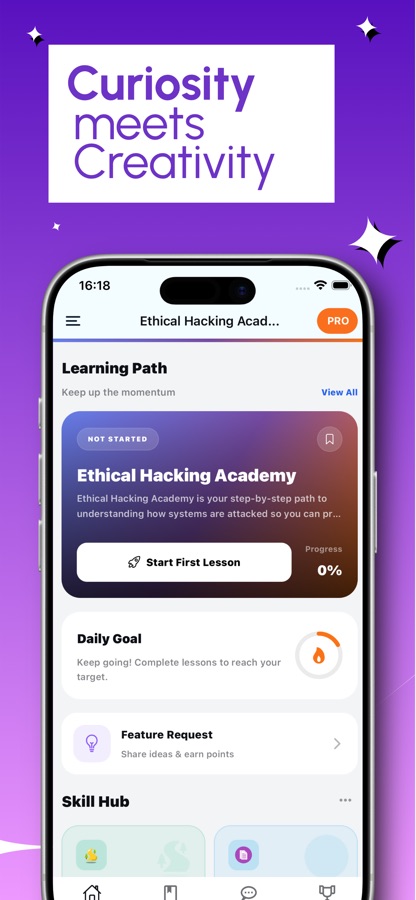
कोर्स
ethical hacking कोर्स में क्या-क्या शामिल है
साइट के एथिकल हैकिंग सीखें कोर्स में 31 courses हैं; ये वे courses हैं जो पहली बार सीखने के लिए इसकी मुख्य रूपरेखा बनाते हैं।
Hacking Lab सेट अप करना और Hackers के लिए Linux
Virtualization की बुनियादी बातें, Kali Linux इंस्टॉल करना, Linux file system और वे ज़रूरी commands जिनका इस्तेमाल आप बाद के हर कोर्स में करेंगे।
Networking Fundamentals, Cryptography और Windows Internals
डेटा कैसे यात्रा करता है और कौन-से protocols महत्वपूर्ण हैं, encoding और encryption में अंतर, hashing, तथा Windows का architecture और registry।
Footprinting, Scanning और Nmap Deep Dive
किसी target के बारे में intelligence जुटाना, फिर host discovery, port scanning techniques और मिलने वाली services की enumeration।
Metasploit, Burp Suite और Password Cracking
Metasploit framework का architecture और exploit workflow, Burp Suite में web requests को proxy और replay करना, तथा wordlists, rules और Hashcat।
Privilege Escalation और Active Directory Attacks
Linux पर enumeration, SUID और sudo का दुरुपयोग, Windows पर service misconfigurations, और Kerberoasting के ज़रिए Active Directory की बुनियादी बातें।
Web, Wireless, Mobile और Cloud Pentesting
Web application hacking, wireless network testing, Android app analysis और cloud attack surface, जिसमें IAM misconfigurations भी शामिल हैं।
Bug Bounty Hunting और Penetration Testing & Reporting
Targets चुनना और बड़े पैमाने पर recon करना, फिर skills को एक structured test और ऐसी report में जोड़ना जिस पर client कार्रवाई कर सके।
यह कैसे काम करता है
Study session कैसे काम करता है
app learning और doing को अलग रखता है, इसलिए हर topic एक short lesson के तुरंत बाद run, predict या fix करने वाली किसी activity से जुड़ा होता है।
Short lesson में method सीखें
learning path से कोई course चुनें और plain language में लिखा lesson पढ़ें। साथ में AI mentor तैयार रहता है, जो आपके समझ में न आने वाले किसी भी tool, technique या error message को समझा सकता है।
Simulated target पर practice करें
pentest lab में आप guided mission को step by step पूरा करते हैं: commands टाइप करते हैं, output पढ़ते हैं और objective की ओर बढ़ते हैं; अटकने पर hints मिलते हैं। Command drills यह जाँचते हैं कि आपके flags वास्तव में काम करेंगे या नहीं।
Review करें, मुकाबला करें और certify हों
Quizzes, review cards, cheat sheets और command book पहले पढ़ी सामग्री को ताज़ा रखते हैं। Live arena और head-to-head matches competition जोड़ते हैं, और graded exam verification code वाला certificate जारी करता है।
इसमें क्या है
app के साथ क्या मिलता है
30+
Courses, 110+ lessons
Kali Linux और hackers के लिए Linux के साथ safe lab setup करने से लेकर networking, cryptography और Windows internals तक, और फिर Active Directory attacks, mobile और cloud pentesting तथा buffer overflow basics तक।
Labs
Simulated targets पर Pentest labs
Guided missions, जिनमें आप खुद commands टाइप करते हैं और output पढ़ते हैं, साथ ही nmap, gobuster, sqlmap, hydra और john के लिए command drills, जो जाँचते हैं कि आपके flags सही तरह काम करते हैं या नहीं।
AI
AI mentor
किसी भी tool, technique या error के बारे में पूछें और स्पष्ट explanation पाएँ। Mentor, Pro का हिस्सा है।
Toolbox
Flag Lab और Hash & Encoding Lab
किसी tool के flags को on और off करके देखें कि हर flag क्या करता है, hash की पहचान करें, encoding की layers हटाएँ और wordlist strategy चुनें।
Arena
Live arena और head-to-head
Worldwide round दिन में तीन बार चलता है, और आप किसी दूसरे learner का head-to-head match में सामना कर सकते हैं।
Exam
Graded exam और certificate
Final exam verification code वाला certificate of completion जारी करता है, जिसे कोई भी verify कर सकता है। यह इसी app का certificate है, किसी third-party certification का नहीं।
पृष्ठभूमि
penetration test क्या होता है और हर phase में क्या होता है?
penetration test किसी system में सेंध लगाने का एक authorised और scoped प्रयास है, ताकि उसका owner किसी वास्तविक attacker के खोजने से पहले weaknesses को ठीक कर सके। इसे एक निश्चित क्रम में किया जाता है, ताकि परिणाम ऐसा report हो जिस पर कोई कार्रवाई कर सके, न कि tricks का ढेर। उस क्रम को पहले सीखना ही किसी security practitioner को ऐसे व्यक्ति से अलग करता है जिसने केवल tools इकट्ठे किए हों।
Reconnaissanceपहले target को जानें
tester target के बारे में सार्वजनिक रूप से उपलब्ध जानकारी इकट्ठी करता है: domains, staff, technologies और exposed services। Open-source intelligence (OSINT) और footprinting इसी चरण में होते हैं, किसी ऐसे packet को भेजने से पहले जो alarm पैदा कर सकता हो।
Scanning और enumerationखुले दरवाज़े खोजें
Nmap जैसे tools यह map करते हैं कि कौन से hosts active हैं, कौन से ports जवाब देते हैं और कौन से service versions चल रहे हैं। फिर enumeration अधिक जानकारी के लिए हर service से पूछताछ करता है, क्योंकि old version banner अक्सर पहला वास्तविक सुराग होता है।
Exploitation और privilege escalationसाबित करें कि कमजोरी वास्तविक है
एक confirmed vulnerability का इस्तेमाल foothold हासिल करने के लिए किया जाता है, आमतौर पर low-privileged user के रूप में। फिर escalation ऐसी misconfigurations खोजता है, जैसे weak sudo rules या unquoted service paths, जो उस foothold को administrator access में बदल देती हैं।
Reportingजिसके लिए clients भुगतान करते हैं
हर finding को evidence, severity rating और concrete fix के साथ लिखा जाता है। technically brilliant test भी vague report के साथ कुछ नहीं बदलता, इसलिए reporting को अपने आप में एक skill के रूप में सिखाया जाता है।
उपयुक्तता
यह किन लोगों के लिए है — और किनके लिए नहीं
आपके लिए सही है, अगर आप
- क्या आप साइबर सुरक्षा की ओर आकर्षित ऐसे beginner हैं, जिन्हें पता नहीं कि शुरुआत कहाँ से करें
- क्या आप IT या networking में काम करते हैं और अपने resume के लिए pentesting skills चाहते हैं
- क्या आप CTFs, bug bounty programmes या entry-level security exams की तैयारी कर रहे हैं
- क्या आप developer हैं और देखना चाहते हैं कि attackers आपके लिखे code को कैसे तोड़ते हैं
- क्या आप videos देखने के बजाय किसी सुरक्षित lab में commands टाइप करके बेहतर सीखते हैं
आपके लिए सही टूल नहीं है, अगर आप
- क्या आप ऐसे systems पर हमला करना चाहते हैं जिनके आप मालिक नहीं हैं, जबकि यह कोर्स केवल authorised testing सिखाता है
- क्या आप third-party certification की उम्मीद रखते हैं, जबकि certificate ऐप की ओर से दिया जाने वाला completion certificate है
- क्या आप सब कुछ मुफ्त चाहते हैं, जबकि पहला course और पहली labs मुफ्त हैं और Pro बाकी सब unlock करता है
- क्या आपको real virtual machines वाली पूरी desktop lab चाहिए, जिसके लिए अब भी laptop की ज़रूरत होगी
सवाल
अक्सर पूछे जाने वाले सवाल
फोन पर hacking course के लिए सबसे अच्छा app कौन-सा है?
ऐसा app चुनें जो recon से reporting तक एक real penetration test का पालन कराए और केवल पढ़ने के बजाय आपको अभ्यास करवाए। एथिकल हैकिंग सीखें में 30+ courses और 110+ lessons हैं, जो इसी क्रम का पालन करते हैं। इसके अलावा simulated targets पर pentest labs, command drills और एक graded exam भी है। iOS और Android पर शुरुआत करना मुफ्त है।
क्या ethical hacking सीखना कानूनी है?
इन techniques को सीखना कानूनी है। लेकिन ऐसे systems पर उनका इस्तेमाल करना जिनके आप मालिक नहीं हैं, या लिखित अनुमति के बिना उनका इस्तेमाल करना कानूनी नहीं है। एथिकल हैकिंग सीखें हर lab को simulated, sandboxed target पर चलाता है और स्पष्ट रूप से बताता है कि आपको केवल उन्हीं systems का परीक्षण करना चाहिए जिनके आप मालिक हैं या जिनके परीक्षण के लिए आपको authorised किया गया है।
क्या शुरुआत से पहले मुझे Linux या networking की जानकारी होना ज़रूरी है?
Hacking का कोई पूर्व अनुभव ज़रूरी नहीं है। एथिकल हैकिंग सीखें की शुरुआत ethical hacking क्या है, कानूनी बुनियादी नियम और Kali Linux के साथ सुरक्षित lab सेट अप करने से होती है। इसके बाद scanning और exploitation से पहले Linux for hackers और networking fundamentals सिखाए जाते हैं।
कोर्स में कौन-से tools सिखाए जाते हैं?
एथिकल हैकिंग सीखें में Kali Linux, Nmap, Metasploit, Burp Suite, Hashcat और John the Ripper शामिल हैं। साथ ही nmap, gobuster, sqlmap, hydra और john के लिए command drills भी हैं। उद्देश्य यह समझना है कि test के हर चरण में कौन-सा tool किस सवाल का जवाब देता है।
फोन पर pentest labs कैसे काम करती हैं?
हर pentest lab एक simulated target के विरुद्ध guided mission होती है। आप commands टाइप करते हैं, output पढ़ते हैं और objective को step by step पूरा करते हैं; अटकने पर hints मिलते हैं। इसके बाद Findings feature आपकी खोजों को एक finding card में बदल देता है, ठीक वैसे ही जैसे pentest report में होता है।
क्या एथिकल हैकिंग सीखें मुझे bug bounty hunting के लिए तैयार करता है?
यह आपको बुनियादी आधार देता है। एक dedicated Bug Bounty Hunting course में targets चुनना, बड़े पैमाने पर recon करना और सामान्य bugs ढूँढना शामिल है, जबकि web courses में SQL injection और XSS सिखाए जाते हैं। Real programmes के अपने rules और scopes होते हैं, इसलिए किसी भी चीज़ का testing करने से पहले उन्हें पढ़ें।
क्या एथिकल हैकिंग सीखें मुफ्त है?
इसे मुफ्त में download किया जा सकता है। पहला course पूरी तरह मुफ्त है और catalogue की पहली labs खुली हैं। Pro हर course और lab, AI mentor और certification exam को unlock करता है तथा banner ads हटा देता है।
क्या certificate को मान्यता प्राप्त security certification माना जाता है?
नहीं। Graded exam पास करने पर ऐप की ओर से completion certificate मिलता है, जिसमें verification code होता है जिसे कोई भी जाँच सकता है। यह आपके किए गए काम का प्रमाण है और projects के साथ उपयोगी है, लेकिन यह third-party certification नहीं है।
क्या मैं दूसरे learners के विरुद्ध अभ्यास कर सकता हूँ?
हाँ। Live arena में दुनिया भर के learners के लिए दिन में तीन बार round होता है और head-to-head matches में आपका मुकाबला किसी दूसरे learner से होता है। अकेले revision के लिए quizzes, review cards, interview questions, cheat sheets और glossary भी उपलब्ध हैं।
यह किन languages और platforms को support करता है?
एथिकल हैकिंग सीखें iOS और Android पर चलता है और 22 languages में उपलब्ध है। इसे App Store पर 4+ rating मिली है और iPhone पर इसे iOS 15.1 या बाद का version चाहिए।
शुरू करें
आज ही अपनी पहली लैब चलाएँ
iOS और Android पर 22 भाषाओं में शुरुआत निःशुल्क करें।
CoddyKit की ओर से और
iOS और Android पर उपलब्ध है।